Keeping Env Files and Private Keys Out of Release Archives
Packing scripts are often written as “take this folder and archive it”. That’s fine until the folder holds more than it should. A developer runs the release script locally once, with a .env file sitting in the build folder because the integration tests needed it. A signing step drops its key file next to the program it just signed. A Mac adds .DS_Store files to every folder it opens.
Once a release is public, a secret inside it is public too, and deleting the release doesn’t take it back: mirrors, caches and package managers may already have copies. The only safe time to catch it is before publishing.
What rmqa Looks For
Every archive rmqa opens is checked against a forbid list. By default it catches:
.env .env.* *.pem *.key id_rsa id_ed25519 .git/* .npmrc .pypirc
That’s environment files, private keys and certificates, SSH keys, a whole .git folder (with its history), and the config files npm and PyPI keep tokens in. A pattern without a slash matches at any depth, so *.key catches certs/signing.key too.
Separately, rmqa warns about clutter: .DS_Store, __MACOSX/, Thumbs.db, editor backup files. Those aren’t dangerous, but they show an archive was packed by hand, from a folder nobody cleaned.
The Check
Here a release of the made-up tool tidy was packed from two working folders that had picked up extra files:
Checking dist for tidy 2.3.0

  ok    tidy_darwin_amd64.tar.gz  darwin/amd64
  FAIL  tidy_darwin_arm64.tar.gz  darwin/arm64
          certs/signing.key: should never ship in a release (it looks like a secret, a key or private config) [forbidden-file]
          warning: .DS_Store: is clutter from the machine that packed the archive [junk-file]
  FAIL  tidy_linux_amd64.tar.gz   linux/amd64
          .env: should never ship in a release (it looks like a secret, a key or private config) [forbidden-file]
  ok    tidy_linux_arm64.tar.gz   linux/arm64
  ok    tidy_windows_amd64.zip    windows/amd64
  ok    SHA256SUMS

Not ready: 2 errors, 1 warning in 6 files.
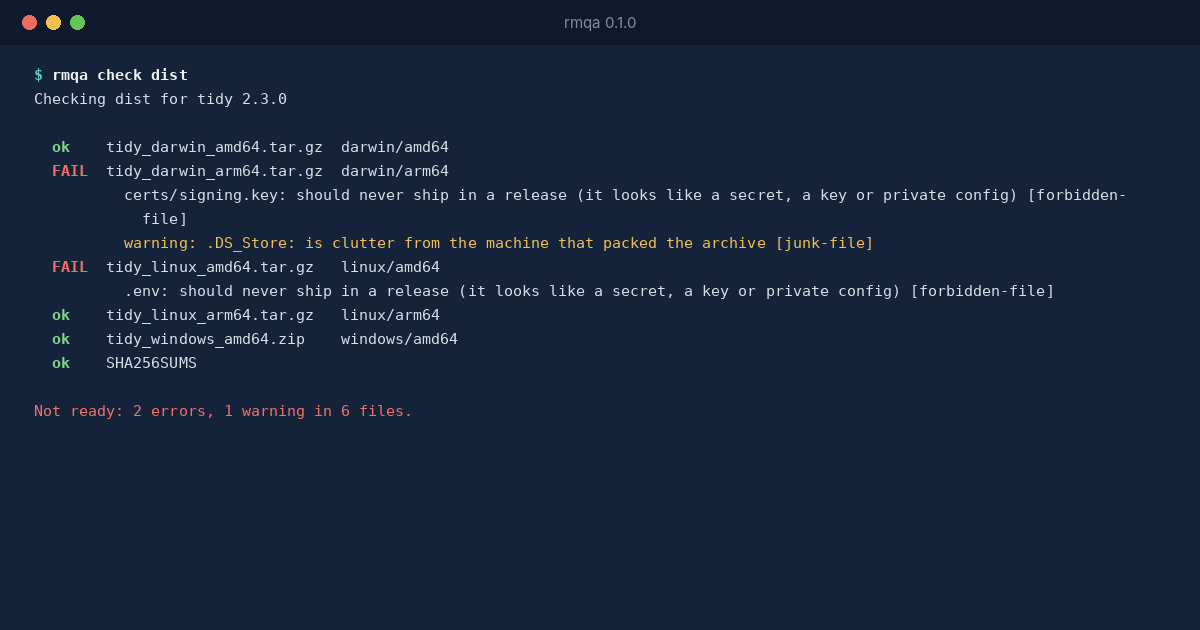
Both secrets are errors, so the release stops. The .DS_Store is a warning: it doesn’t stop the release unless you run with --strict.
Your Own List
Projects have their own secrets. Set forbid in the manifest to replace the default list, and keep the defaults you want:
forbid = [".env", ".env.*", "*.pem", "*.key", "id_rsa", "id_ed25519", ".git/*",
          "*.p12", "*.keystore", "credentials.json", "terraform.tfstate"]
The Other Half: Paths That Escape
The same pass checks every entry’s path. An entry named ../../.bashrc, an absolute path, or a link pointing outside the archive would write outside the folder a user unpacks into. This is the “zip slip” problem, and some unpacking tools don’t guard against it. rmqa reports each such entry as unsafe-path. It’s rare in honest releases, which is exactly why it’s worth a check: when it shows up, something is badly wrong with the packing step.